Can search history be seen through wifi bill documentation
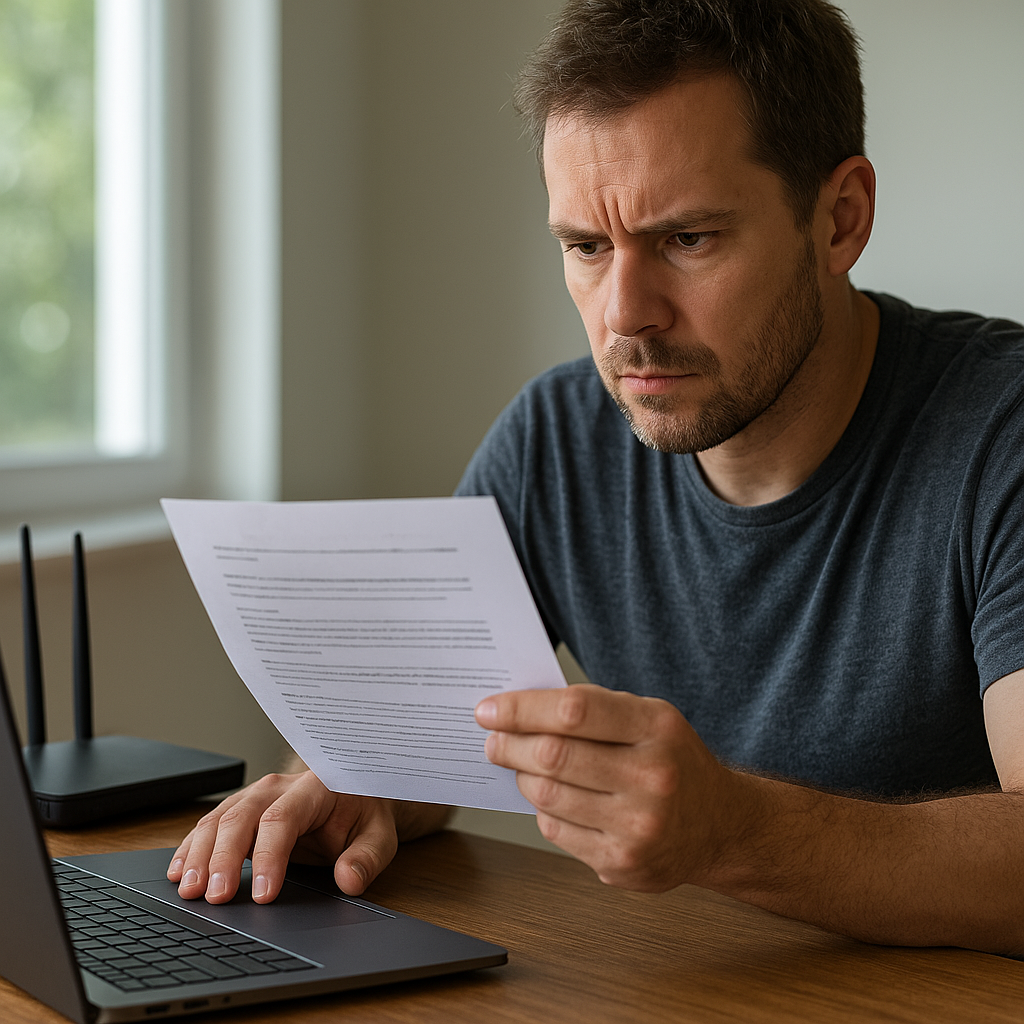
Households routinely review monthly invoices to track data usage and plan limits. The recurring question stems from a common misunderstanding of how carriers separate accounting from network routing. Service providers genereate financial statements strictly for capacity monitoring. They do not log individual queries or transmit browsing details to billing departments. This architectural split has existed since broadband replaced dial-up, keeping consumer inquiries private while allowing accurate bandwidth tracking.
Can your parents see your search history through wifi bills
Family plans often list multiple connected devices and total gigabytes consumed, but the paper or digital statement never reveals specific websites visited. When someone asks this, the answer remains consistent across major North American and European carriers. Invoices reflect aggregate consumption patterns, not granular activity. Even detailed usage breakdowns stop at domain categories or peak-hour notifications. Financial records handle monetary transactions, while network telemetry operates on a completely different infrastructure.
Can u see your search history on the wifi bill
The shorthand phrasing surfaces frequently in household discussions. Technical documentation clarifies that billing systems process metered data volumes, not content inspection. Modern encryption standards wrap every session in secure tunnels that mask the actual payload from financial processors. A carrier only records that four gigabytes moved through a household gateway. The exact search terms, video streams, or messaging traffic remain invisible to anyone reading the invoice. Only local network administrators with router access might notice traffic spikes, but the statement itself contains nothing beyond numerical values.
Network operators deliberately isolate financial documentation from traffic inspection. Billing statements reflect capacity, not content. This structural separation has protected everyday browsing habits since the early broadband era and remains standard practice across regulated markets.
| Record Type | Shows Specific Queries | Tracks Bandwidth | Lists Connected Devices |
|---|---|---|---|
| Monthly Carrier Invoice | Never | Always | Rarely |
| Router Admin Panel | Partial | Yes | Always |
| ISP Account Dashboard | Never | Yes | Sometimes |
| Local Browser Cache | Always | No | No |
Can the wifi bill show search history under modern encryption standards
The transition from unsecured HTTP to mandatory HTTPS fundamentally altered what external parties can observe. Earlier networks occasionally transmitted requests in plain text, making theoretical interception possible. Today, end-to-end encryption wraps every session before it reaches the carrier gateway. When evaluating this scenario, the answer hinges on how data travels. Financial processors only handle encrypted byte counts. They do not decrypt headers or parse URL strings. Even if a household administrator reviews the invoice, the document remains completely detached from actual browsing behavior.
Can you see people’s search history on wifi bill records
Shared networks naturally spark visibility concerns between users. The exact concern appears in countless tech discussions, yet carrier documentation stays uniform. Monthly statements aggregate household consumption into a single line item. They never break down activity by individual endpoint or user account. Network owners accessing local router configurations might observe connected device names and traffic volumes, but the financial record stays entirely separate. Modern browsers also implement strict cookie partitioning and DNS over HTTPS, further isolating queries from network-level monitoring. Anyone checking teh invoice will only see numbers and service descriptions.
- Check local router logs for device tracking rather than relying on carrier invoices
- Enable encrypted DNS protocols to prevent network-level query logging
- Review browser privacy settings to limit local cache retention
- Understand that billing departments never recieve packet inspection data
Internet privacy frameworks shifted dramatically over the past twenty years. Dial-up connections in the late nineties exposed every request to telephone carriers and early service providers. Billing operated on time-based metrics, and activity logs occasionally surfaced during troubleshooting. Broadband introduced flat-rate plans, shifting carrier focus toward bandwidth caps and network optimization. By the mid-2010s, HTTPS adoption became mandatory across major platforms, severing the link between visible invoices and actual browsing habits. Automated content filtering and encrypted DNS tunnels now make it practically impossible for financial documents to reveal personal queries. The industry moved from transparent logging to strict data compartmentalization, ensuring statements serve accounting purposes rather than oversight functions. Federal Trade Commission Privacy Guidelines and ETSI Security Standards Framework outline current consumer protections. Reference material: Source: bbc.com.